


[Sep-2026] Verified 300-720 dumps Q&As - 300-720 dumps with Correct Answers
The Best CCNP Security Study Guide for the 300-720 Exam
Cisco 300-720 exam consists of 60-70 multiple-choice questions and has a duration of 90 minutes. To pass the exam, candidates must score at least 70%. 300-720 exam can be taken at any authorized testing center and is available in multiple languages.
NEW QUESTION # 116
Which component must be added to the content filter to trigger on failed SPF Verification or DKIM Authentication verdicts?
- A. condition
- B. status
- C. parameter
- D. response
Answer: A
Explanation:
Condition is a component that must be added to the content filter to trigger on failed SPF Verification or DKIM Authentication verdicts. Condition is a criterion that determines whether a message matches a content filter rule or not, such as message size, sender address, attachment type, etc.
To add a condition to the content filter that triggers on failed SPF Verification or DKIM Authentication verdicts, the administrator can follow these steps:
Select Mail Policies > Content Filters and click Add Filter.
Enter a name and description for the content filter.
Under Conditions, click Add Condition.
Choose SPF Verification or DKIM Authentication from the drop-down menu.
Choose Fail from the drop-down menu.
Click Submit.
The other options are not valid components to trigger on failed SPF Verification or DKIM Authentication verdicts, because they are not part of content filters.
NEW QUESTION # 117
Refer to the exhibit. Which configuration on the scan behavior must be updated to allow the attachment to be scanned on the Cisco ESA?
- A. Add an additional mapping for attachment type for zip files.
- B. Increase the maximum recursion depth from 5 to a larger value.
- C. Increase the maximum attachment size to scan to a larger value.
- D. Enable assume match pattern if the email was not scanned for any reason.
Answer: C
Explanation:
The maximum attachment size to scan is a configuration on the scan behavior that determines the maximum size of an attachment that Cisco ESA will scan for viruses and malware. If an attachment exceeds this size, Cisco ESA will apply the configured action for unscannable messages, such as deliver, drop, or quarantine.
To allow the attachment to be scanned on the Cisco ESA, this configuration must be updated to a larger value than the attachment size, which is 10 MB according to the message header.
The other options are not valid configurations to allow the attachment to be scanned on the Cisco ESA, because they do not affect the maximum attachment size to scan.
NEW QUESTION # 118
An analyst creates a new content dictionary to use with Forged Email Detection.
Which entry will be added into the dictionary?
- A. [email protected]
- B. ^Alpha\ Beta$
- C. mycompany.com
- D. Alpha Beta
Answer: D
Explanation: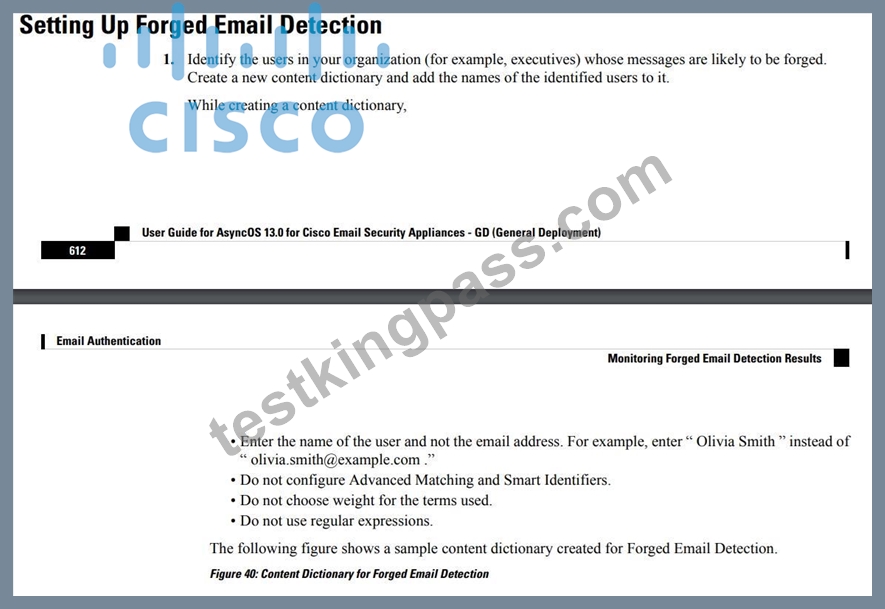
https://www.cisco.com/c/en/us/td/docs/security/esa/esa13-
0/user_guide/b_ESA_Admin_Guide_13-0.pdf p.675
NEW QUESTION # 119
An administrator identifies that, over the past week, the Cisco ESA is receiving many emails from certain senders and domains which are being consistently quarantined. The administrator wants to ensure that these senders and domain are unable to send anymore emails.
Which feature on Cisco ESA should be used to achieve this?
- A. blocklist
- B. safelist
- C. S/MIME Sending Profile
- D. incoming mail policies
Answer: D
NEW QUESTION # 120
A Cisco ESA administrator was notified that a user was not receiving emails from a specific domain. After reviewing the mail logs, the sender had a negative sender-based reputation score.
What should the administrator do to allow inbound email from that specific domain?
- A. Modify the firewall to allow emails from the domain.
- B. Create a new inbound mail policy with a message filter that overrides Talos.
- C. Ask the user to add the sender to the email application's allow list.
- D. Add the domain into the allow list.
Answer: D
NEW QUESTION # 121
An engineer must enable Domain-based Message Authentication, Reporting and Conformance (DMARC) in Cisco Secure Email Gateway. Messages that fail the DMARC verification must be rejected by using SMTP Code 550 with response:
#5.7.1 DMARC unauthenticated mail is prohibited.
Which action must be taken after creating the DMARC verification profile?
- A. Apply the policy with the quarantined DMARC record, AsyncOS must quarantine the record.
- B. Implement the policy with the rejected DMARC record, AsyncOS must reject the record.
- C. When messages temporarily fail during DMARC verification, AsyncOS should reject the record.
- D. Configure the policy with the quarantined DMARC record, AsyncOS must reject the record.
Answer: B
Explanation:
After creating the DMARC verification profile, the administrator must apply a DMARC policy action for domains whose DMARC record specifies reject. Configuring AsyncOS to reject those failed messages enforces the sender domain's DMARC policy and allows the appliance to return the required SMTP 550 response.
NEW QUESTION # 122
Which antispam feature is utilized to give end users control to allow emails that are spam to be delivered to their inbox, overriding any spam verdict and action on the Cisco ESA?
- A. end user allow list
- B. end user safelist
- C. end user passthrough list
- D. end user spam quarantine access
Answer: B
Explanation: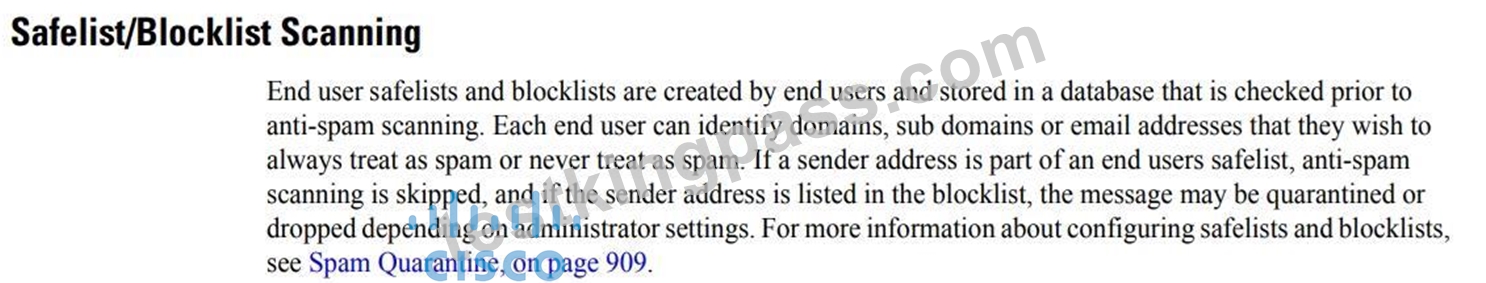
https://www.cisco.com/c/en/us/td/docs/security/esa/esa13-
0/user_guide/b_ESA_Admin_Guide_13-0.pdf P.129
NEW QUESTION # 123
Spreadsheets containing credit card numbers are being allowed to bypass the Cisco ESA.
Which outgoing mail policy feature should be configured to catch this content before it leaves the network?
- A. file reputation filtering
- B. outbreak filtering
- C. file analysis
- D. data loss prevention
Answer: D
Explanation:
Data Loss Prevention (DLP) is an outgoing mail policy feature that should be configured to catch this content before it leaves the network. DLP allows Cisco ESA to scan outgoing messages for sensitive or confidential data, such as credit card numbers, social security numbers, health records, etc., and apply appropriate actions, such as encrypt, quarantine, notify, etc., to prevent data leakage or loss.
The other options are not valid outgoing mail policy features to catch this content before it leaves the network, because they do not scan for sensitive or confidential data in messages.
References: User Guide for AsyncOS 15.0 for Cisco Secure Email Gateway, page 9-2 and page 9-3.
NEW QUESTION # 124
Which two are configured in the DMARC verification profile? (Choose two.)
- A. message action to take when the policy is reject/quarantine
- B. name of the verification profile
- C. minimum number of signatures to verify
- D. ESA listeners to use the verification profile
- E. message action into an incoming or outgoing content filter
Answer: A,B
Explanation:
A DMARC verification profile is a list of parameters that the mail flow policies of the appliance use for verifying DMARC. The name of the verification profile identifies the profile and allows you to apply it to different mail flow policies. The message action to take when the policy is reject/quarantine determines how the appliance handles messages that fail DMARC verification based on the sender's DMARC policy.
NEW QUESTION # 125
Drag and Drop Question
An engineer must provide user access to the spam quarantine on a Cisco Secure Email Gateway. Users must be able to access the spam quarantine without additional authentication by using links. The users must be able to preview a spam message from within the Spam Quarantine section without restoring the message. Drag and drop the actions from the left into sequence on the right to meet the requirements.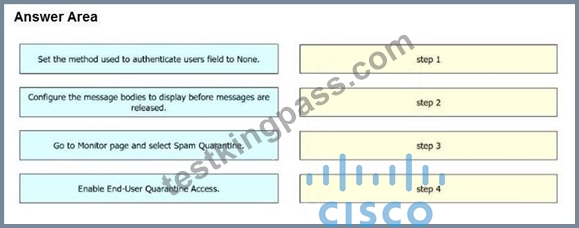
Answer:
Explanation:
Explanation:
You begin by navigating to the Spam Quarantine settings, enable user access, configure authentication to None for link-based access, and then set up message preview for users.
NEW QUESTION # 126
A company has deployed a new mandate that requires all emails sent externally from the Sales Department to be scanned by DLP for PCI-DSS compliance. A new DLP policy has been created on the Cisco ESA and needs to be assigned to a mail policy named `Sales' that has yet to be created.
Which mail policy should be created to accomplish this task?
- A. Outgoing Mail Policy
- B. Outgoing Mail Flow Policy
- C. Incoming Mail Flow Policy
- D. Preliminary Mail Policy
Answer: A
Explanation:
Overview of Mail Policies
The appliance enforces your organization's policies for messages sent to and from your users through the use of mail policies. These are sets of rules that specify the types of suspect, sensitive, or malicious content that your organization may not want entering or leaving your network. This content may include:
spam
legitimate marketing messages
graymail
viruses
phishing and other targeted mail attacks
confidential corporate data
personally identifiable information
https://www.cisco.com/c/en/us/td/docs/security/esa/esa11-1/user_guide/b_ESA_Admin_Guide_11_1/b_ESA_Admin_Guide_chapter_01001.html
NEW QUESTION # 127
An engineer deploys a Cisco Secure Email Gateway appliance with default settings in an organization that permits only standard H feature does not work. Which additional action resolves the issue?
- A. Enable the Use HTTP option under Advanced Settings for File Reputation.
- B. TP/HTTPS ports outbound and notices that the AMP file reputation
- C. Enable the Use SSL option under Advanced Settings for File Reputation.
- D. Configure the outbound firewall rule to permit traffic on port 8081
- E. Configure the outbound firewall rule to permit traffic on port 3237
Answer: B
Explanation:
Configuring the outbound firewall rule to permit traffic on port 3237 is the additional action that resolves the issue. AMP file reputation is a feature that allows Cisco ESA to check files attached to messages against a cloud-based database of known malicious files and apply appropriate actions, such as block, deliver, or quarantine.
By default, AMP file reputation uses TCP port 3237 to communicate with the cloud-based database. If this port is blocked by a firewall, AMP file reputation will not work properly. To resolve this issue, the administrator can configure the outbound firewall rule to permit traffic on port 3237 from Cisco ESA.
NEW QUESTION # 128
Which two action types are performed by Cisco ESA message filters? (Choose two.)
- A. discard actions
- B. filter actions
- C. quarantine actions
- D. non-final actions
- E. final actions
Answer: D,E
NEW QUESTION # 129
Which two configurations are used on multiple LDAP servers to connect with Cisco ESA? (Choose two.)
- A. active-active
- B. load balancing
- C. SLA monitor
- D. failover
- E. active-standby
Answer: B,D
Explanation:
You can enter multiple host names to configure the LDAP servers for failover or load-balancing. Separate multiple entries with commas.
Reference:
https://www.cisco.com/c/en/us/td/docs/security/ces/user_guide/sma_user_guide/ b_SMA_Admin_Guide_ces_11/b_SMA_Admin_Guide_chapter_01010.html
NEW QUESTION # 130
A security engineer wants to ensure that legitimate emails from [email protected] are not quarantined as spam in Cisco Secure Email. Which action must be taken to meet this requirement?
- A. Add the domain to the allowlist.
- B. Add all partners.com email addresses to the allowlist.
- C. Add the domain to the safelist.
- D. Remove the domain from the Wocklist.
Answer: C
NEW QUESTION # 131
Which two statements about configuring message filters within the Cisco ESA are true? (Choose two.)
- A. Message filters configuration within the web user interface is located within Incoming Content Filters.
- B. Message filters can be configured only from the web user interface.
- C. The filters command executed from the CLI is used to configure the message filters.
- D. The filterconfig command executed from the CLI is used to configure message filters.
- E. Message filters can be configured only from the CLI.
Answer: C,E
NEW QUESTION # 132
Which process is skipped when an email is received from safedomain.com, which is on the safelist?
- A. message filter
- B. antispam scanning
- C. outbreak filter
- D. antivirus scanning
Answer: A
NEW QUESTION # 133
A Cisco ESA administrator has several mail policies configured. While testing policy match using a specific sender, the email was not matching the expected policy.
What is the reason of this?
- A. The message header with the highest priority is checked against each policy in a top-down fashion.
- B. The "From" header is checked against all policies in a top-down fashion.
- C. The "To" header is checked against all policies in a top-down fashion.
- D. The message header with the highest priority is checked against the Default policy in a top-down fashion.
Answer: B
Explanation:
First Match Wins
Each user (sender or recipient) is evaluated for each mail policy defined the appropriate mail policy table in a top-down fashion.
https://www.cisco.com/c/en/us/td/docs/security/esa/esa11-1/user_guide/b_ESA_Admin_Guide_11_1/b_ESA_Admin_Guide_chapter_01001.html?bookSear ch=true
NEW QUESTION # 134
Drag and drop the AsyncOS methods for performing DMARC verification from the left into the correct order on the right.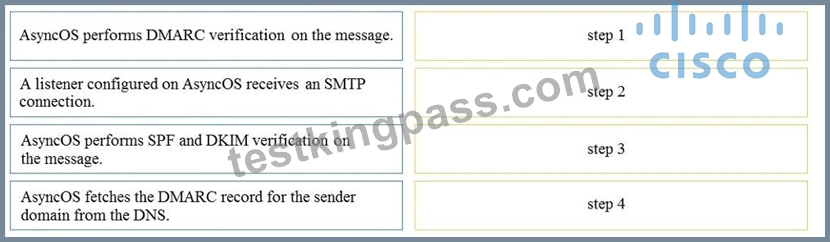
Answer:
Explanation: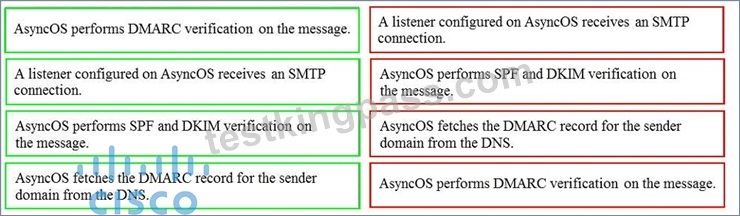
Reference:
https://www.cisco.com/c/en/us/td/docs/security/esa/esa11-1/user_guide/b_ESA_Admin_Guide_11_1/ b_ESA_Admin_Guide_11_1_chapter_010101.html
NEW QUESTION # 135
......
What is the Registration procedure of the Cisco 300-720 Exam
In order to apply for the Cisco 300-720 Exam, You have to follow
- Step 1: Visit to Pearson VUE Exam Registration
- Step 2: Signup/Login to Pearson VUE account
- Step 3: Search for Cisco 300-720 Certifications Exam
- Step 4: Select Date, time and confirm with a payment method
300-720 certification guide Q&A from Training Expert TestkingPass: https://evedumps.testkingpass.com/300-720-testking-dumps.html